
Ledger has confirmed that unauthorized hardware implants found in some cryptocurrency signers sold by Southeast Asian reseller CryptoBilis could capture users’ 24-word recovery phrases and send them over a mobile network. The company says the implants operated separately from the wallets’ normal security systems and did not change how transactions were signed.
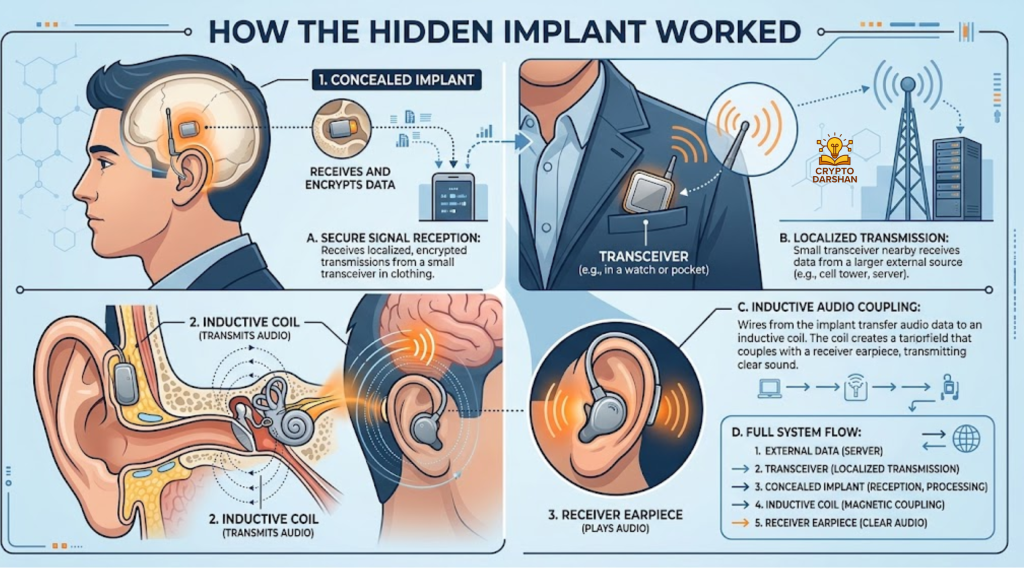
How the hidden implant worked
Ledger’s security team, Donjon, began investigating after customers reported missing cryptocurrency on October 9. By October 10, the team had found an unauthorized component inside a device belonging to one affected customer.
The implant was hidden inside the wallet’s casing and could monitor what appeared on the device’s screen. During initial setup, a signer displays a 24-word recovery phrase—the set of words that can restore access to a crypto wallet. The implant used a microcontroller to read those screens, decode the recovery words, and transmit them through an LTE connection using a provisioned eSIM.
In simple terms, the chip acted like a hidden camera for the wallet’s screen. It did not need to break into the Secure Element, the chip that protects private keys. Instead, it captured the recovery phrase while the user was setting up the device.
What the implant did not change
Ledger says the implant did not modify the Secure Element, the Ledger operating system, cryptocurrency transactions, or digital signatures. That means the device could still appear to work normally when signing transactions.
The danger came from the recovery phrase. Anyone who obtains those 24 words can restore a wallet on another device and control its funds. Once the implant sent the phrase to an attacker, the attacker would not need access to the physical wallet to drain the account.
it has not yet identified how the components were installed, who installed them, or whether the issue affects devices sold through other channels. The company said it has not verified a fund loss linked to a signer bought elsewhere, although its researchers continue to examine reports involving modified hardware.
CryptoBilis suspends wallet sales
The investigation centers on devices sold through CryptoBilis, a Ledger reseller serving Southeast Asian markets. After It received reports of stolen funds, it asked the distributor to stop selling and shipping the affected products.
CryptoBilis has suspended sales of Ledger signers while investigators examine devices and reported customer losses. It says every fund loss it has verified so far involved devices purchased through CryptoBilis.
The company has not confirmed the total number of affected users or the total value lost. Blockchain analytics firm Bitquery estimated suspected thefts at about $102 million across 324 wallets, but Ledger says those figures are third-party estimates and have not been fully verified.
What affected users should do
Ledger has told CryptoBilis customers who have not yet initialized their devices to avoid setting them up and to contact Ledger Support first.
For customers who have already used an affected device, Ledger recommends moving their crypto to a new signer initialized with a completely new recovery phrase. The company specifically warns users not to restore their existing recovery words into another device bought from CryptoBilis, because that phrase may already be known to the attacker.
Users who lost funds have been asked to report the incident through Ledger’s official support channels and contact local law enforcement. Ledger also advised people not to send suspected tampered devices to anyone before speaking with Ledger Support or authorities, because the hardware could be important evidence.
Why recovery phrases matter
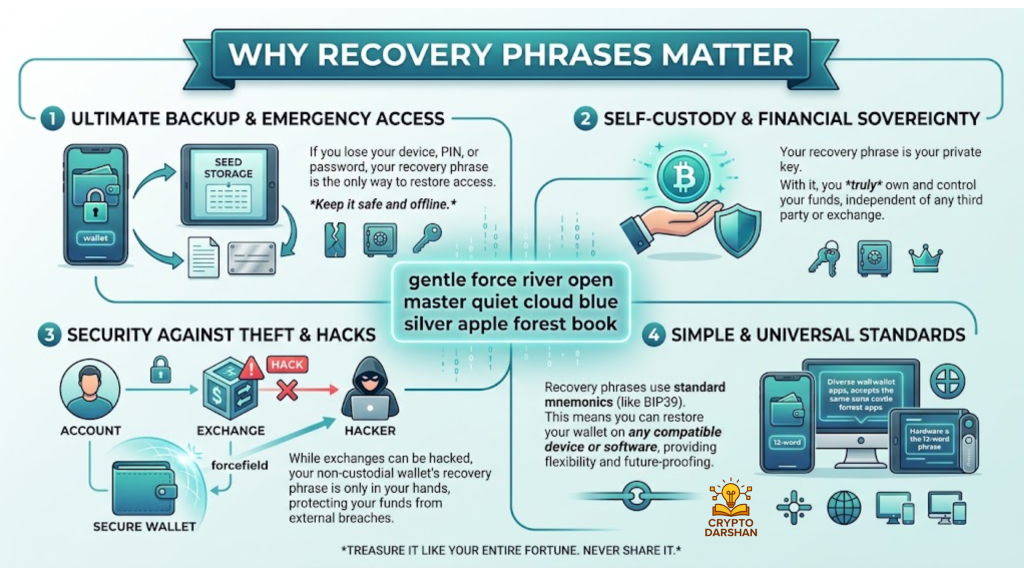
A recovery phrase, sometimes called a seed phrase, is the master backup for a self-custody crypto wallet. It is not a password that can be easily changed. If someone learns it, they can recreate the wallet and access its funds.
This incident shows why users should treat recovery phrases as their most sensitive crypto information. A secure backup should stay offline, remain private, and never be entered into a website, shared in a message, or photographed. Ledger reiterated that it will never call customers, send unsolicited direct messages, or ask for recovery phrases.
Investigation continues
Ledger’s Donjon team is still examining submitted devices, physical modifications, and reports involving other signer models and locations. The company says it will release more information once new findings are verified.
The case highlights a key point for hardware-wallet buyers: the security of a crypto signer depends not only on its software and Secure Element, but also on the supply chain. Buying directly from a manufacturer or an authorized seller can reduce the risk of receiving a device that has been altered before it reaches the customer.