
Blockchain investigator ZachXBT has increased his estimate of a suspected cryptocurrency theft involving an unidentified European entity to more than $133 million. He says the total rose after tracing another $27 million in withdrawals from centralized exchanges, and he has accused the affected organization of failing to disclose the incident.
How the estimate increased
ZachXBT first raised the alarm on November 2, saying an unidentified European entity appeared to have lost more than $106 million from several centralized exchange accounts on November 1. His latest update added four wallet addresses to the investigation, bringing the publicly identified addresses to 15.
The investigator says the newly traced withdrawals were connected to the same illicit actor identified in his earlier findings. Some withdrawals reportedly occurred after he first disclosed the incident publicly.
The $133 million figure is an investigator estimate based on on-chain tracing, not a confirmed loss figure published by the affected institution. No organization has been publicly named, and no regulator or law-enforcement agency has confirmed the full scale of the incident.
Allegations of a cover-up
ZachXBT said the suspected victim may be a major financial institution in Western Europe. He claimed the organization concealed the incident and criticized the lack of a public disclosure.
He also said more than $30 million had already been laundered. In his view, faster disclosure could have allowed European Union law enforcement to freeze some of those funds before they moved further through the crypto ecosystem.
These are allegations, not proven findings. The affected entity has not been identified publicly, and there is no confirmed statement from regulators, law enforcement or the suspected victim verifying the theft or the alleged cover-up.
How the funds were moved
According to ZachXBT’s findings, the attacker first withdrew suspected stolen assets in two dollar-pegged stablecoins: USD Coin (USDC) and Tether (USDT). The funds were then moved through several services in an effort to make them harder to trace.
Over the following 24 hours, some USDC was swapped for Ethereum. Portions of the assets were then sent to instant cryptocurrency exchanges, including WellWallet and Kyrrex.
Another route involved Wagyu, where funds were converted into Monero (XMR), a privacy-focused cryptocurrency that obscures transaction details. The attacker also used blockchain bridges to move assets between different networks.
Moving digital assets across multiple platforms and blockchain networks demonstrates how quickly cryptocurrency transactions can cross borders. Our guide to cross-border payments explores how digital assets are changing international money transfers.
Why investigators doubt Lazarus
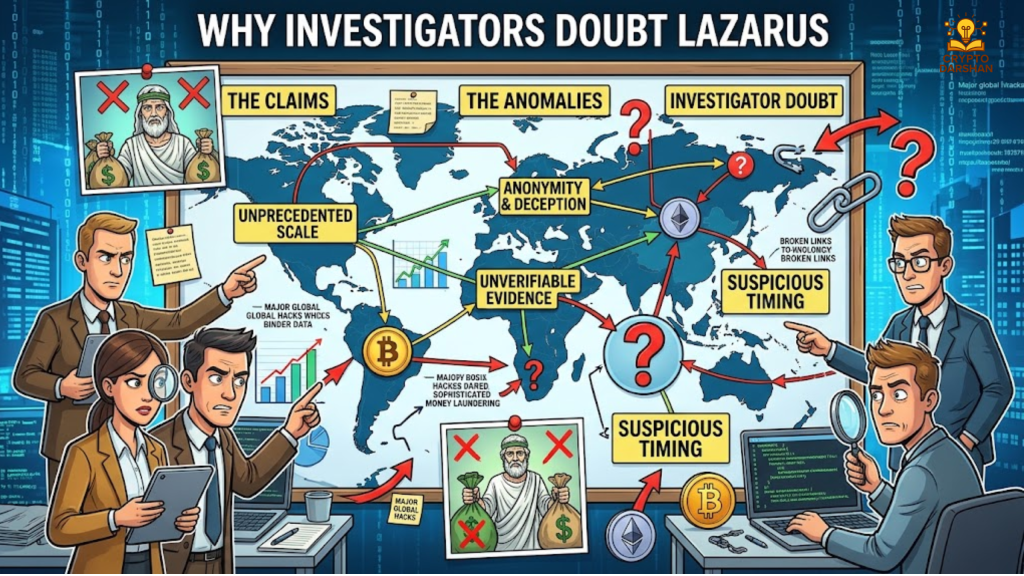
ZachXBT said he is highly confident that North Korea’s Lazarus Group was not responsible. He pointed to differences in the laundering patterns from those he associates with the North Korean-linked group.
In a later post on X, he said the suspected attacker appeared to be French-speaking and had some on-chain connections to users of cybercrime forums. Those observations are investigative leads, not a confirmed identification of the person or group behind the theft.
The absence of a Lazarus link, if confirmed, ZachXBT would distinguish this case from several major crypto thefts previously attributed to North Korean actors.
A familiar laundering pattern
The use of instant exchanges, stablecoins and Monero follows patterns seen in earlier crypto theft investigations. Attackers often convert stolen assets into different tokens, move them across chains, and use privacy tools to reduce the chance that investigators can follow the funds.
In June, ZachXBT traced roughly $120.2 million through crypto services and Monero-related transactions. Tether later froze $72 million in USDT connected to that investigation after blacklisting an address holding about 72.03 million USDT.
That case involved movement through Tron, KuCoin, instant exchanges and NEAR Intents wallets. It shows how stablecoin issuers and exchanges can sometimes freeze assets if they identify suspicious addresses quickly.
Other recent tracing work
ZachXBT’s latest disclosure follows several other investigations into illicit crypto flows. In October, he linked FreedomXMR inflows on Hyperliquid Core to suspected illicit activity, estimating that more than 87% of the service’s incoming funds were connected to illegal sources.
He traced more than $20 million in that investigation to ransomware payments, crypto exploits, malware and social-engineering attacks. The identified transactions included funds linked to incidents involving DCENT Wallet, Fetch.ai, Axelar and gambling platform Gamdom.
In another October investigation, ZachXBT said he infiltrated an alleged Chinese criminal operation connected to laundering funds from North Korean hackers. He claimed the network had processed more than $1 billion tied to the February 2025 Bybit hack.
What happens next
The case remains unresolved. The key questions are whether the suspected victim confirms the loss, whether law enforcement can freeze additional funds, and whether investigators can identify the attacker.
For crypto users and institutions, the incident highlights the importance of rapid disclosure. If funds are reported and flagged quickly, exchanges and stablecoin issuers may have a better chance of freezing assets before they are converted into privacy coins or moved through unregulated services.